- Why [24]7.ai
- Products
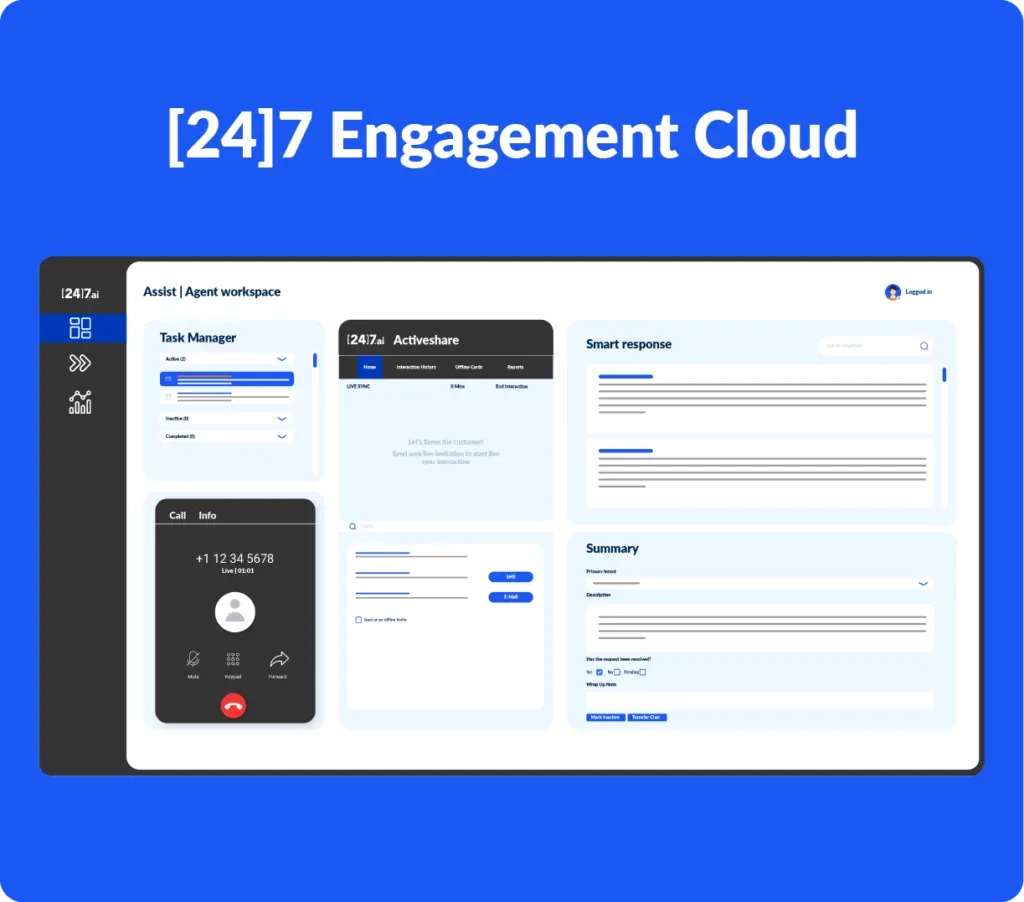
[24]7 Engagement Cloud, an AI-powered omnichannel CX platform, equips you to excel at every stage of the customer journey, from the very first interaction to building enduring relationships. A complete package that helps you acquire new customers, nurture existing ones, and drive long-term retention – all on a single, unified platform.Discover how our platform empowers customers, agents and contact center leaders to deliver exceptional CX: - Services
AI-Driven CX That Delivers
Transform your CX strategy with AI-driven intelligence. Combine passionate CX brand ambassadors, predictive analytics, and intelligent automation to cultivate loyalty, craft unforgettable customer experiences, and deliver measurable business impact at scale.
- Solutions
End-To-End CX Management
Explore by Use Case
US Retailer Transforms CX with [24]7.ai Managed Customer Engagement
Gold Awards at US Customer Experience Awards, 2024
- Company
Explore [24]7.ai
Explore Locations
- Insights
- Careers
Work @ [24]7.ai
Work Locations
- Product Login and Support
- Contact Us
Privacy Policy
Your trust matters. At [24]7.ai, we understand the importance of safeguarding your brand and customer information. We're committed to providing the highest levels of security, privacy, compliance, and responsible AI practices. Explore our Trust Center to learn more about our dedication to earning your trust, every step of the way.
Website Privacy Policy
(last revised on May 05, 2026)
[24]7.ai, Inc., on behalf of itself and its affiliated companies (collectively, “[24]7.ai” or the “Company”), has adopted the following Privacy Policy in furtherance of respecting online privacy and recognizing the need for appropriate protection and management of the personally-identifiable information we may receive from visitors to this United States-based website (“Personal Information”). Specifically, Personal Information means any information relating to an identified or identifiable natural person (‘data subject’); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person.
General Framework
The Company is committed to compliance with all applicable laws, regulations and rules governing the privacy of information it collects and the attendant rights of the subjects of such information. This commitment includes full compliance with the General Data Protection Regulation of the European Union (GDPR) as well as with applicable federal and state requirements of the United States of America, and with applicable laws in the jurisdictions in which we operate.
[24]7.ai complies with the EU-U.S. Data Privacy Framework (EU-U.S. DPF) and the Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF) as set forth by the U.S. Department of Commerce. [24]7.ai has certified to the U.S. Department of Commerce that it adheres to the EU-U.S. Data Privacy Framework Principles (EU-U.S. DPF Principles) with regard to the processing of personal data received from the European Union in reliance on the EU-U.S. DPF. [24]7.ai has certified to the U.S. Department of Commerce that it adheres to the Swiss-U.S. Data Privacy Framework Principles (Swiss-U.S. DPF Principles) with regard to the processing of personal data received from Switzerland. If there is any conflict between the terms in this privacy policy and the EU-U.S. DPF Principles and/or the Swiss-U.S. DPF Principles, the Principles shall govern. To learn more about the Data Privacy Framework (DPF) program, and to view our certification, please visit https://www.dataprivacyframework.gov/.
[24]7.ai is responsible for the processing of personal data it receives, under the DPF, and subsequently transfers to a third party acting as an agent on its behalf. [24]7.ai complies with the DPF Principles for all onward transfers of personal data from the EU and Switzerland, including the onward transfer liability provisions.
The Federal Trade Commission has jurisdiction over [24]7.ai’s compliance with the EU-U.S. DPF and Swiss-U.S. DPF. In certain situations, [24]7.ai may be required to disclose personal data in response to lawful requests by public authorities, including to meet national security or law enforcement requirements.
In compliance with the EU-U.S. DPF and the Swiss-U.S. DPF, [24]7.ai commits to refer unresolved complaints concerning our handling of personal data received in reliance on the EU-U.S. DPF and the Swiss-U.S. DPF to TRUSTe, an alternative dispute resolution provider based in the United States. If you do not receive timely acknowledgment of your DPF Principles-related complaint from us, or if we have not addressed your DPF Principles-related complaint to your satisfaction, please visit https://feedback-form.truste.com/watchdog/request for more information or to file a complaint. These dispute resolution services are provided at no cost to you.
For complaints regarding DPF compliance not resolved by any of the other DPF mechanisms, you have the possibility, under certain conditions, to invoke binding arbitration. Further information can be found on the official DPF website.
APEC Participation
[24]7.ai’s privacy practices, described in this Privacy Policy, comply with the APEC Cross Border Privacy Rules System. The APEC CBPR system provides a framework for organizations to ensure protection of personal information transferred among participating APEC economies. More information about the APEC framework can be found here
Collection of Personal Information
For those persons from the European Economic Area: Under most circumstances, we collect personal information from you only if you have provided consent, or such collection is required in order for us to perform our contractual obligations, or where it is in our or a third party’s legitimate interests, but only if such interests are not outweighed by your data protection interests or fundamental rights and freedoms. There may be certain circumstances where we have a legal obligation to collect personal data, or collecting your data would be to protect your vital interests or those of another person. If you have any questions about the legal basis on which we collect your personal information, please contact us.
This Privacy Policy applies to all information submitted by you (or passively collected from you) on this website, including Personal Information and any information you may have provided through an application for employment either through this website or through a third party (“Applicant data”). There are times, when we may need you to provide Personal Information (such as your name, phone number, email address and postal address) to be able to provide you with the information, service or product you have requested. You may be asked to provide such Personal Information through completing a form on this website. You are not obligated to provide this Personal Information, but you may not be able to get the products, services or information you requested without it.
We may use Personal Information we collect to support our clients in customer engagement and customer acquisition efforts, to contact you regarding a job position for which you have applied, and to optimize customer website experiences on client websites. We may also use your Personal Information to correspond with you or to provide you with information on-line, such as a newsletter. Also, if you provide us with your Personal Information, then we may attempt to contact you, either by phone or email, to see whether we can provide you with additional information or to share information about a product or service that we think you might find interesting. In addition, if you chose to have a business relationship with [24]7.ai, such as a contractual or other business relationship or partnership, we will naturally continue to contact you in connection with that business relationship.
We sometimes monitor who visits this website and for how long (using cookies and other tracking technologies, as described in the next section) and we may attempt to initiate a chat session with this website’s visitors. You may opt out of participating in the chat session by either closing the chat window or responding that you do not care to engage in a chat session.
We may also collect from you, personal information about your contacts such as name and email address in order to forward a job posting. When you provide us with personal information about your contacts, we will only use this information for the specific reason for which it is provided. If you believe that one of your contacts has provided us with your personal information and you would like to request that it be removed from our database, please contact us at webmaster@247.ai.
If you desire to revoke your consent to our use of the data as set forth herein, you may do so by contacting us at webmaster@247.ai. Upon receipt of notification from you, we will no longer collect or use the personal data as set forth herein, but will retain personal information as long as needed to comply with our legal and business obligations.
International Transfer of Personal Information
[24]7.ai stores Personal Information in the United States. It is possible that we may transfer and access Personal Information from other countries where [24]7.ai has operations. If this is the case, [24]7.ai will transfer Personal Information in conformity with guidelines set forth in the Data Privacy Framework. Use of our website constitutes agreement to the transfer of any Personal Information we collect from you to the United States and/or other countries in which we operate. [24]7.ai commits to cooperate with EU data protection authorities (DPAs) and the Swiss Federal Data Protection and Information Commissioner (FDPIC) and comply with the advice given by such authorities with regard to human resources data transferred from the EU and Switzerland in the context of the employment relationship.
Cookies, IP Addresses and Other Tracking Technologies
Some parts of this website utilize “cookies” and other third party tracking technologies (such as beacons, tags, and scripts) to analyze trends, administer the site, track users’ movements around the site, to collect information about your activity on this and other websites, and gather demographic information about our user base as a whole. You can control the use of cookies at the individual browser level, but if you disable the use of cookies, it may limit your use of certain features or functions on our website or service. Some cookies and other technologies may serve to recall Personal Information previously supplied or collected by you.
Another method through which we collect aggregate information is the collection of IP addresses. An IP address is a unique number that is automatically assigned to your computer when you access the Internet. Web servers automatically identify your computer by its IP address. When you access this website, our, and our third party analytics as well as other partners, web servers log your IP address. Other tracking technologies may record information such as Internet domain and host names you visit before and after visiting this website; browser software and operating system types; button click patterns; and dates and times that this website is accessed. Our use of cookies and other tracking technologies allows us to improve this website. We may also analyze information that does not contain Personal Information for trends and statistics.
We and our third party tracking-utility partners utilize (i) a 1×1 image tracking pixel placed on certain webpages of the website to collect relevant information from this website and to set a Cookie on your web browser, (ii) your browser stream data to the this website, or (iii) other information collected from you (collectively, the “Targeting Data”). Such Targeting Data may include, among other things, IP address, date and time of your visit to this website, and website pages visited by you. We tie the information gathered by clear gifs to our customers’ personally identifiable information. The Targeting Data is used to provide our targeted advertisements to you while you are on third-party websites with whom we have purchased advertising inventory and may be combined or matched to third party data to identify you and display a targeted advertisement to you.
Personal Preference
You may request information on how your Personal Information is being retained or processed by us or a third party, how to access, request deletion, and review your Personal Information, or request to obtain a copy of the Personal Information we hold, by sending an inquiry to webmaster@247.ai. In responding to requests for a copy of the Personal Information we hold, we will provide such information in a commonly used format that is machine-readable, such as a PDF file.
In some cases you have a right to erasure of Personal Information we hold. However, we may need to retain certain information to comply with our legal or business obligations.
If you tell us that you do not wish to have your Personal Information used as a basis for further contact with you, we will respect your wishes. You may choose to opt-out of receiving future e-mail or mailings by following the unsubscribe procedures generally provided with our communications, or by sending an email to webmaster@247.ai specifying “Unsubscribe” in the subject line.
We partner with a third party to either display advertising on our website or to manage our advertising on other sites. Our third party partner may use cookies or similar technologies in order to provide you advertising based upon your browsing activities and interests. If you wish to opt out of interest-based advertising click here (or if located in the European Union click here). Please note you will continue to receive generic ads. If you clear your web browser’s cookies and then visit this website again, or visit this website from a different web browser, you will need to re-enter your opt-out choices.
Data Security
We utilize a combination of reasonable and appropriate physical, technical, and administrative safeguards to prevent unauthorized access or disclosure, to maintain data accuracy of your Personal Information, and to ensure the appropriate use of Personal Information we collect and process via this website. [24]7.ai retains Personal Information only as required or permitted by local law and while it has a legitimate business purpose to do so. When you enter non-sensitive Personal Information (such as your name, email address, company and geography), as requested by forms on our website, it is not encrypted.
Accuracy of Personal Information
[24]7.ai intends to maintain accurate Personal Information at all times. If you require the Personal Information you have provided [24]7.ai to be updated, or that we delete inaccuracies you may send updates and corrections to [24]7.ai via email to webmaster@247.ai specifying in the Subject line that you wish to provide an update and we will make reasonable efforts to incorporate the changes in our records as soon as practicable, if you provide the information we require to locate your Personal Information in our records (e.g. old name, email address, etc.). Once we make the requested update, we will send you an e-mail confirmation so that you are aware the update or correction has been made. If you requested to update your e-mail address or mailing address, we will send the confirmation notice to both the old and new addresses. If you wish to cancel your account or request that we no longer use your information to provide you services contact us via the information above. We will respond to your requests for access within a reasonable amount of time.
Third Parties
Occasionally, we may share aggregate, non-personally identifiable information about our users with our business and alliance partners. We also use third party service providers such as an email service provider to send emails on our behalf and an employment partner to process job applications. Other than our business and alliance partners, we do not provide Personal Information to any third party for any purpose whatsoever other than as outlined in this Privacy Policy, and we will not do so unless we are legally required to do so and when we believe that disclosure is necessary to protect our rights and/or to comply with a judicial proceeding, court order, or legal process served on our website. Similarly, it is against our policy to sell Personal Information collected online without consent. We will take reasonable steps to ensure that third-parties who receive any of your Personal Information from us protect such information on [24]7.ai’s behalf.
In the event [24]7.ai goes through a business transition, such as a merger, acquisition by another company, or sale of all or a portion of its assets, your personally identifiable information will likely be among the assets transferred. You will be notified via email or a prominent notice will be displayed on our website for 30 days of any such change in ownership or control of your personal information.
Links to Other Websites
When you are on this website, you could be directed to other websites that are beyond our control. There may be links to other websites that take you outside our service; for example, links to business/alliance partners and trade show companies. These other websites may send their own cookies to users, or otherwise collect data or solicit personal information. If you are directed to any third-party website, we make no representation as to the existence, sufficiency, accuracy or completeness of the privacy policy of the companies associated with such websites.
Social Media Features
Our website may include links to Social Media websites, such as Facebook, LinkedIn or Twitter. These Social Media websites may collect your IP address, which page you are visiting on our site, and may set a cookie. Social Media websites are hosted by a third party. Your interactions with these Social Media websites are governed by the privacy policy of the company providing it.
Blogs
Our website offers blogs where visitors may submit comments that may be published when approved by [24]7.ai. You should be aware that any information you provide in these areas may be read, collected, and used by others who access them. To request removal of your personal information from our blog, contact us at webmaster@247.ai. In some cases, we may not be able to remove your personal information, in which case we will let you know if we are unable to do so and why.
Children's Privacy
This website is not designed to attract children. Accordingly, we do not intend to collect Personal Information from anyone we know to be under 13 years of age.
STATEMENT OF CONSENT
BY USING THIS WEBSITE OR BY SUBMITTING AN APPLICATION FOR EMPLOYMENT, YOU CONSENT TO THE TERMS OF THIS PRIVACY POLICY AND TO [24]7.AI PROCESSING AND USING PERSONAL INFORMATION FOR THE PURPOSES DESCRIBED HEREIN.
Changes
Should this Privacy Policy change, we intend to take reasonable steps to ensure that these changes are brought to your attention by posting a revised Privacy Policy on this website. If we make any material changes we will notify you by email (sent to the e-mail address specified in your account) or by means of a prominent notice on this Site prior to the change becoming effective.
Contact Information
For questions about this Privacy Policy, please write to privacy@247.ai or to:
[24]7.ai, Inc
Attn: Legal Department
2105 S.Bascom Ave.
Suite 195, Campbell,
CA 95008, USA
Platform Privacy
(last revised on May 05, 2026)
[24]7.ai, Inc and its affiliates (collectively, “[24]7.ai”) provide software platforms, applications, and data analysis systems (collectively, the “[24]7.ai Platform”) which enable [24]7.ai’s clients (DEFINE as “Client”) to better service their current and prospective customers (each an “End User”) via the Internet and telephony networks. This [24]7.ai Platform Privacy Policy is applicable to those Clients and End Users who are either directly or indirectly using the [24]7.ai Platform.
At the contractual direction of [24]7.ai’s clients, [24]7.ai collects and processes End User’s information which may include Personal Information, where “Personal Information” means information that can be used to specifically identify an End User, including, but not limited to, a first and last name, organization name, email address, phone number, postal/zip or other physical address, date of birth, gender, professional title, account information, credit/debit card number, and any other such information needed by the [24]7.ai Platform to provide client-specified services to an End User. [24]7.ai respects the privacy of End Users and is committed to protecting the Personal Information that we receive through their direct and indirect use of the [24]7.ai Platform. Notwithstanding the foregoing, End Users’ use of our clients’ Internet- and telephony- based services (and, ultimately, the [24]7.ai Platform) is solely governed by the terms and conditions agreed to directly between End Users and [24]7.ai’s clients (usually via a signed written agreement, “Terms of Use” and/or a “Privacy Policy” on such clients’ websites).
Collection and Use of Information
Certain information about End Users is passively collected through the [24]7.ai Platform without those End Users actively providing that information to [24]7.ai (“Interaction Data”). Collection of Interaction Data is done using various technologies, such as website cookies (see section on cookies below), Internet/web tags, and navigational data collection (e.g. website log files, server logs, etc.). We do not consider Interaction Data to be Personal Information.
Some Interaction Data is automatically transmitted by End Users’ Internet web browsers and telephony networks to the [24]7.ai Platform, with examples including: the URL of the website an End User browsed before accessing the [24]7.ai Platform; the Internet Protocol (“IP”) address of the End User’s computer (a unique number automatically assigned to an End User’s computer when connecting to the Internet, which may vary from session to session); the web browser version that the End User’s computer or mobile device is currently using; the date and time the End User accessed the website or online service; and the specific webpages that an End User accessed while visiting the website. Interaction Data is used by [24]7.ai for internal purposes, to analyze trends, and to improve the [24]7.ai Platform. [24]7.ai also uses Interaction Data to improve our clients’ web, mobile and telephony systems. For example, Interaction Data is collected and used to personalize websites so that their content, layout, functionality, navigation, recommendations, offers and promotions will be more relevant to End Users based on their collective or individual context.
Before using the [24]7.ai Platform, we agree in written contracts with our clients that they have sufficient rights, including their End Users’ consent, to allow us to collect both Personal Information and Interaction Data. If you have any concerns about one of our client’s right to collect such data from you and to pass it on to [24]7.ai, please contact that client directly.
We collect the following kinds of personal information from our Clients:
- Contact Information such as name, email address, mailing address, phone number
- Billing Information such as billing address
- Unique Identifiers such as user name and account number
We use this information to provide Clients:
- Relevant account or product information
- Assistance in completing transactions
- Resolution to customer service issues
[24]7.ai collects information under the direction of its clients, and has no direct relationship with the individuals whose personal data it processes.
Cookies
[24]7.ai uses “cookies” or similar technologies to track and collect End Users’ Personal Information and Interaction Data. A “cookie” is a small data file that [24]7.ai transfers to an End User’s computer or mobile device for various tracking purposes. [24]7.ai uses these cookies to save relevant data to enhance End Users’ experiences while on our clients’ websites. End Users may set their web browser to notify them when a cookie is sent, or to refuse cookies altogether, but certain features of the [24]7.ai Platform (and of our clients’ websites) might not work well or at all if cookies are blocked or deleted. Before using the [24]7.ai Platform, our clients promise us that they have their End Users’ consent to set/collect cookies (or for [24]7.ai to set/collect the cookies on their behalf) and that they have the right to give such information to [24]7.ai to process on their behalf. If you have any concerns about one of our client’s right to set/collect cookies or to give us the right to do so on their behalf, please contact that client directly.
Opt-Out
Before using the [24]7.ai Platform, we agree in written agreements with our clients that they have sufficient rights, including their End Users’ consent, to allow us to collect both Personal Information and Interaction Data. End Users who do not wish to have their Personal Information or Interaction Data collected should contact our client directly or visit our client’s privacy policy for guidance on opting out. Please note that End Users who clear their web browser’s cookies and then visit our client’s website again, or visit our client’s website from a different web browser, may need to re-enter their opt-out choices with our client. If you are a client and would like to update your account please contact us via your client account representative.
We will send you strictly service-related announcements on rare occasions when it is necessary to do so. For instance, if our service is temporarily suspended for maintenance, we might send you an email.
Generally, you may not opt-out of these communications, which are not promotional in nature. If you do not wish to receive them, you have the option to deactivate your account.
Security
The [24]7.ai Platform follows industry standards to protect the security of End Users’ Personal Information and [24]7.ai respects End Users’ choices for such information’s intended use (to the extent those choices are communicated to our clients by End Users and then onward-communicated by our clients to us). We utilize a combination of reasonable and appropriate physical, technical, and administrative safeguards to prevent unauthorized access or disclosure of End Users’ Personal Information, to maintain data accuracy of End Users’ Personal Information, and to ensure the appropriate use of End Users’ Personal Information we collect and process. [24]7.ai retains Personal Information and Interaction Data only as required or permitted by local law and while it has a legitimate business purpose. In addition, [24]7.ai uses standard security protocols, and mechanisms to exchange the transmission of sensitive Personal Information such as credit card details and login credentials. End Users submit sensitive Personal Information such as their credit card number in the [24]7.ai Platform via functionality which limits the sensitive data from being persisted by [24]7.ai and is encrypted using transport layer security (“TLS”) technology.
Data Privacy Framework(DPF) Principles
End Users’ information may be stored, processed and/or accessed in the United States or in any other country in which [24]7.ai or its affiliates, subsidiaries or agents maintain facilities. By using the [24]7.ai Platform, our clients have promised us that such End Users have consented to any such transfer of information outside of the End Users’ home country.
We and our wholly owned subsidiaries 24/7 Customer Private Limited, Tellme Networks, Inc., [24]7 US LLC, [24]7.ai,Inc. comply with the EU-U.S. Data Privacy Framework (EU-U.S. DPF) and the Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF) as set forth by the U.S. Department of Commerce. [24]7.ai has certified to the U.S. Department of Commerce that it adheres to the EU-U.S. Data Privacy Framework Principles (EU-U.S. DPF Principles) with regard to the processing of personal data received from the European Union in reliance on the EU-U.S. DPF. [24]7.ai has certified to the U.S. Department of Commerce that it adheres to the Swiss-U.S. Data Privacy Framework Principles (Swiss-U.S. DPF Principles) with regard to the processing of personal data received from Switzerland. If there is any conflict between the terms in this privacy policy and the EU-U.S. DPF Principles and/or the Swiss-U.S. DPF Principles, the Principles shall govern. To learn more about the Data Privacy Framework (DPF) program, and to view our certification, please visit https://www.dataprivacyframework.gov/.
[24]7.ai is responsible for the processing of personal data it receives, under the DPF, and subsequently transfers to a third party acting as an agent on its behalf. [24]7.ai complies with the DPF Principles for all onward transfers of personal data from the EU and Switzerland, including the onward transfer liability provisions.
The Federal Trade Commission has jurisdiction over [24]7.ai’s compliance with the EU-U.S. DPF and Swiss-U.S. DPF. In certain situations, [24]7.ai may be required to disclose personal data in response to lawful requests by public authorities, including to meet national security or law enforcement requirements.
In compliance with the EU-U.S. DPF and the Swiss-U.S. DPF, [24]7.ai commits to refer unresolved complaints concerning our handling of personal data received in reliance on the EU-U.S. DPF and the Swiss-U.S. DPF to TRUSTe, an alternative dispute resolution provider based in the United States. If you do not receive timely acknowledgment of your DPF Principles-related complaint from us, or if we have not addressed your DPF Principles-related complaint to your satisfaction, please visit https://feedback-form.truste.com/watchdog/request for more information or to file a complaint. These dispute resolution services are provided at no cost to you.
For complaints regarding DPF compliance not resolved by any of the other DPF mechanisms, you have the possibility, under certain conditions, to invoke binding arbitration. Further information can be found on the official DPF website.
Accuracy of Personal Information
[24]7.ai has no direct relationship with the individuals whose personal data it processes. [24]7.ai endeavors to maintain accurate Personal Information at all times but ultimately is reliant on its clients for the accuracy of Personal Information. If an End User requires updates to her/his Personal Information or requests their data be deleted/deactivated in the [24]7.ai Platform, the End User should request such changes directly through our applicable client, and [24]7.ai will make reasonable efforts to incorporate such changes, or respond to requests for access, deletion, correction, amendment, restriction in the [24]7.ai Platform within 30 days.
Onward Transfer
The [24]7.ai Platform operates globally. Therefore, [24]7.ai may transfer End Users’ Personal Information and Interaction Data on to its affiliates and/or subcontractors worldwide for the purpose of further processing or storage, and/or may transfer data within its control to various geographies as part of its own processing efforts. [24]7.ai will not sell, rent, transfer or lease an End User’s Personal Information to any third party except with the End User’s direct consent, whether provided directly or relayed to us by our clients Transfers to any third parties are covered by the provisions in this Policy regarding notice and choice and the service agreements with our Clients; the transfer is to other [24]7.ai entities and/or business partners who are acting on behalf of [24]7.ai for the uses described in this policy; or the transfer is required by law or court order, and when we believe that disclosure is necessary to protect our rights and/or to comply with a judicial proceeding, court order, or legal process served on our website.
In the event [24]7.ai goes through a business transition, such as a merger, acquisition by another company, or sale of all or a portion of its assets, your personally identifiable information will likely be among the assets transferred. You will be notified via prominent notice on our website for 30 days of any such change in ownership or control of your personal information.
APEC Participation
[24]7.ai’s privacy practices, described in this Privacy Policy, comply with the APEC Cross Border Privacy Rules System. The APEC CBPR system provides a framework for organizations to ensure protection of personal information transferred among participating APEC economies. More information about the APEC framework can be found here.
Children's Privacy
[24]7.ai Customer Engagement Platform does not intend to target, and is not intended to attract, children under the age of 13. [24]7.ai does not knowingly collect personal data from children under the age of 13 or send requests to children for personal data.
Changes to this Privacy Policy
[24]7.ai may amend this policy from time to time. If we make any material changes in the way we use End Users’ Personal Information we will make that information available by posting a notice on our website prior to the change becoming effective. We encourage you to periodically review this page for the latest information on our privacy practices.
Contact Information
For questions about this [24]7.ai policy, End Users are encouraged to contact our client who has retained us to provide the [24]7 Customer Engagement Platform on their behalf. Such End Users may also write to privacy@247.ai or to:
[24]7.ai, Inc
Attn: Legal Department
2105 S.Bascom Ave.
Suite 195, Campbell,
CA 95008, USA
Privacy Notice for California Residents
Last Updated on February 3rd, 2026
This Privacy Notice for California Residents supplements the information contained in [24]7’s Privacy Policy and applies solely to all visitors, users, and others who reside in the State of California. We adopted this notice to comply with the California Consumer Privacy Act of 2018 (CCPA) and any terms defined in the CCPA have the same meaning when used in this notice.
1. Information We Collect
Our website collects information that identifies, relates to, describes, references, is capable of being associated with, or could reasonably be linked, directly or indirectly, with a particular consumer or device (“personal information”). Our website has collected the following categories of personal information from its consumers within the last twelve (12) months:
Category | Examples | Collected |
| A. Identifiers. | A real name, alias, postal address, unique personal identifier, online identifier, Internet Protocol address, email address, account name, Social Security number, driver’s license number, passport number, or other similar identifiers. | ![]() |
| B. Personal information categories listed in the California Customer Records statute (Cal. Civ. Code § 1798.80(e)). | A name, signature, Social Security number, physical characteristics or description, address, telephone number, passport number, driver’s license or state identification card number, insurance policy number, education, employment, employment history, bank account number, credit card number, debit card number, or any other financial information, medical information, or health insurance information. Some personal information included in this category may overlap with other categories. | ![]() |
| C. Protected classification characteristics under California or federal law. | Age (40 years or older), race, color, ancestry, national origin, citizenship, religion or creed, marital status, medical condition, physical or mental disability, sex (including gender, gender identity, gender expression, pregnancy or childbirth and related medical conditions), sexual orientation, veteran or military status, genetic information (including familial genetic information). | ![]() |
| D. Commercial information. | Records of personal property, products or services purchased, obtained, or considered, or other purchasing or consuming histories or tendencies. | ![]() |
| E. Biometric information. | Genetic, physiological, behavioral, and biological characteristics, or activity patterns used to extract a template or other identifier or identifying information, such as fingerprints, faceprints, and voiceprints, iris or retina scans, keystroke, gait, or other physical patterns, and sleep, health, or exercise data. | |
| F. Internet or other similar network activity. | Browsing history, search history, information on a consumer’s interaction with a website, application, or advertisement. | ![]() |
| G. Geolocation data. | Physical location or movements. | ![]() |
| H. Sensory data. | Audio, electronic, visual, thermal, olfactory, or similar information. | |
| I. Professional or employment-related information. | Current or past job history or performance evaluations. | ![]() |
| J. Non-public education information (per the Family Educational Rights and Privacy Act (20 U.S.C. Section 1232g, 34 C.F.R. Part 99)). | Education records directly related to a student maintained by an educational institution or party acting on its behalf, such as grades, transcripts, class lists, student schedules, student identification codes, student financial information, or student disciplinary records. | |
| K. Inferences drawn from other personal information. | Profile reflecting a person’s preferences, characteristics, psychological trends, predispositions, behavior, attitudes, intelligence, abilities, and aptitudes. |
Personal information does not include:
- Publicly available information from government records.
- Deidentified or aggregated consumer information.
- Information excluded from the CCPA’s scope, like certain health or medical information and other categories of information protected by different laws.
We obtain the categories of personal information listed above from the following categories of sources:
- Directly from you. For example, from forms you complete or products and services you purchase.
- Indirectly from you. For example, from observing your actions on our website.
2. Use of Personal Information
We may use or disclose the personal information we collect for one or more of the following business purposes:
- To fulfill or meet the reason you provided the information. For example, if you share your name and contact information to request a price quote or ask a question about our services, we will use that personal information to respond to your inquiry. If you provide your personal information to purchase a product or service, we will use that information to process your payment and facilitate delivery. We may also save your information to facilitate new product orders or process returns.
- To process your requests, purchases, transactions, and payments and prevent transactional fraud.
- To provide you with support and to respond to your inquiries, including to investigate and address your concerns and monitor and improve our responses.
- To respond to law enforcement requests and as required by applicable law, court order, or governmental regulations.
- As described to you when collecting your personal information or as otherwise set forth in the CCPA.
- To evaluate or conduct a merger, divestiture, restructuring, reorganization, dissolution, or other sale or transfer of some or all of our or our affiliates’ assets in which personal information held by us or our affiliates about our website users is among the assets transferred.
We will not collect additional categories of personal information or use the personal information we collect for materially different, unrelated, or incompatible purposes without providing you notice.
3. Sharing Personal Information
We may disclose your personal information to a third party for a business purpose allowed under the act like identifiers, Personal information categories listed in the California Customer Records statute (Cal. Civ. Code § 1798.80(e)), Commercial information, Internet or other similar network activity and Professional or employment-related information.
When we disclose personal information for a business purpose, we enter a contract that describes the purpose and requires the recipient to both keep that personal information confidential and not use it for any purpose except performing the contract.
We share your personal information with the following categories of third parties:
- Service providers.
- Data Aggregators.
4. Your Rights and Choices
The CCPA provides consumers (California residents) with specific rights regarding their personal information. This section describes your CCPA rights and explains how to exercise those rights.
Access to Specific Information and Data Portability Rights
You have the right to request that we disclose certain information to you about our collection and use of your personal information over the past 12 months. Once we receive and confirm your verifiable consumer request (see Exercising Access, Data Portability, and Deletion Rights), we will disclose to you:
- The categories of personal information we’ve collected about you.
- The categories of sources for the personal information we’ve collected about you.
- The categories of third parties with whom we share that personal information.
- The specific pieces of personal information we’ve collected about you (also called a data portability request).
Deletion Request Rights
You have the right to request that we delete any of your personal information that we collected from you and retained, subject to certain exceptions. Once we receive and confirm your verifiable consumer request (see Exercising Access, Data Portability, and Deletion Rights), we will delete (and direct our service providers to delete) your personal information from our records, unless an exception applies.
We may deny your deletion request if retaining the information is necessary for us or our service provider(s) to:
- Complete the transaction for which we collected the personal information, provide a good or service that you requested, take actions reasonably anticipated within the context of our ongoing business relationship with you, or otherwise perform our contract with you.
- Detect security incidents, protect against malicious, deceptive, fraudulent, or illegal activity, or prosecute those responsible for such activities.
- Debug products to identify and repair errors that impair existing intended functionality.
- Comply with the California Electronic Communications Privacy Act (Cal. Penal Code § 1546 seq.).
- Enable solely internal uses that are reasonably aligned with consumer expectations based on your relationship with us.
- Comply with a legal obligation.
- Make other internal and lawful uses of that information that are compatible with the context in which you provided it.
Exercising Access, Data Portability, and Deletion Rights
To exercise the access, data portability, and deletion rights described above, please submit a verifiable consumer request to us by: Emailing us at Privacy@247.ai.
Only you, or a person registered with the California Secretary of State that you authorize to act on your behalf, may make a verifiable consumer request related to your personal information. You may also make a verifiable consumer request on behalf of your minor child.
You may only make a verifiable consumer request for access or data portability twice within a 12-month period. The verifiable consumer request must:
- Provide sufficient information that allows us to reasonably verify you are the person about whom we’ve collected personal information or an authorized representative.
- Describe your request with sufficient detail that allows us to properly understand, evaluate, and respond to it.
We cannot respond to your request or provide you with personal information if we cannot verify your identity or authority to make the request and confirm the personal information relates to you.
Making a verifiable consumer request does not require you to create an account with us.
We will only use personal information provided in a verifiable consumer request to verify the requestor’s identity or authority to make the request.
Response Timing and Format
We endeavor to respond to a verifiable consumer request within forty-five (45) days of its receipt. If we require more time, we will inform you of the reason and extension period in writing.
We will deliver our written response by mail or electronically, at your option.
Any disclosures we provide will only cover the 12-month period preceding the verifiable consumer request’s receipt. The response we provide will also explain the reasons we cannot comply with a request, if applicable. For data portability requests, we will select a format to provide your personal information that is readily useable and should allow you to transmit the information from one entity to another entity without hindrance.
We do not charge a fee to process or respond to your verifiable consumer request unless it is excessive, repetitive, or manifestly unfounded. If we determine that the request warrants a fee, we will tell you why we made that decision and provide you with a cost estimate before completing your request.
Personal Information Sales
We have never sold your personal information in last 12 months and will not sell your personal information to any party. If in the future, we anticipate any change, we will provide you with the opt-out and opt-in rights required by the CCPA.
5. Non-Discrimination
We will not discriminate against you for exercising any of your CCPA rights. Unless permitted by the CCPA, we will not:
- Deny you goods or services.
- Charge you different prices or rates for goods or services, including through granting discounts or other benefits, or imposing penalties.
- Provide you a different level or quality of goods or services.
- Suggest that you may receive a different price or rate for goods or services or a different level or quality of goods or services.
6. Other California Privacy Rights
California’s “Shine the Light” law (Civil Code Section § 1798.83) permits users of our website that are California residents to request certain information regarding our disclosure of personal information to third parties for their direct marketing purposes. To make such a request, please send an email to Privacy@247.ai.
7. Changes to Our Privacy Notice
Should this Privacy Policy change, we intend to take reasonable steps to ensure that these changes are brought to your attention by posting a revised Privacy Policy on this website. If we make any material changes we will notify you by email (sent to the e-mail address specified in your account) or by means of a prominent notice on this Site prior to the change becoming effective.
We reserve the right to amend this privacy notice at our discretion and at any time. When we make changes to this privacy notice, we will post the updated notice on our website and update the notice’s effective date. Your continued use of our website following the posting of changes constitutes your acceptance of such changes.
8. Contact Information
If you have any questions or comments about this notice, the ways in which we collect and use your information described below and in our Privacy Policy, your choices and rights regarding such use, or wish to exercise your rights under California law, please do not hesitate to contact us at:
Website: www.247.ai
Email: Privacy@247.ai
GDPR Compliance
(last revised on April 22, 2026)
[24]7.ai is committed to respecting all applicable individual rights to privacy including but not limited to rights set forth under the General Data Protection Regulation of the European Union (the “GDPR”). Accordingly, information security, protection of all confidential material entrusted to us, and transparency with respect to individuals who may elect to entrust information to us, are all of the utmost importance to our organization. The following summary sets forth some of the key measures we have set in place to effectuate that commitment, and to meet the enhanced standards for transparency and accountability for personal data uses under the GDPR.
We use personal information in a variety of ways across our products and organization. Specific uses are identified for users of particular products and/or those who elect to use our services, but in general our products and policies limit our collection and use of personal data to online identifiers such as IP address, cookie and device identifiers. We use this information to support our clients in customer engagement and customer acquisition efforts, and to optimize customer website experiences on client websites.
To support all such uses, we have implemented a comprehensive cross-functional effort calculated to ensure full compliance with the GDPR with respect to any role in which we handle sensitive data, whether as controller or processor. Our program includes detailed administrative, technical and operational controls designed to effectuate GDPR principles in all our relevant processes. We have further set in place measures designed to safeguard the data under our care using secure encryption technologies. We also take steps to independently test our security against international standards using third-party auditors. Additional actions we are taking include:
- Implementing new internal controls calculated to enable full compliance with the GDPR and to strengthen the Company’s commitment to respecting all lawful privacy rights;
- Setting in place consent mechanisms to facilitate user consent and withdrawal of consent as appropriate;
- Implementing Privacy by Design in our internal systems and products on an ongoing basis;
- Implementing processes to enable data subjects to exercise their lawful privacy rights with respect to their data;
- Reviewing contracts and contacts with partners to confirm satisfaction of all applicable privacy requirements, including the GDPR;
- In circumstances where we operate as a processor, supporting the controller with respect to all requirements, including data subject rights, incident response, and other matters, in accordance with GDPR Article 28;
- Ensuring that controllers for whom we operate as processors confirm that their instructions are proper and in accord with consents they have secured for the use of data;
- In circumstances where we operate as a controller, ensuring that appropriate consents and/or contractual rights are secured for all uses of personal data;
- Enhancing policies across the organization to ensure compliance and readiness to address any issues, including data subject requests and/or data incidents.
In addition to the measures already set in place, we strive for continuous improvement and therefore review and improve our systems on an ongoing basis. Questions concerning the Company’s GDPR compliance efforts and/or any related matters may be directed to Privacy@247.ai.
[24]7.ai Connect
Last Revised on December 01, 2022
This privacy policy has been compiled to better serve those who are concerned with how their ‘Personally Identifiable Information’ (PII) is used online by using [24]7.ai Connect application. The [24]7.ai Connect Privacy Policy is applicable to all the employees of [24]7.ai Inc. and its affiliates (collectively, “[24]7.ai”) and non- employees who use [24]7.ai Connect application.
[24]7.ai Connect application facilitates notifications and self-serve options from various applications & tools used at [24]7.ai Inc. and its affiliates. Notifications may just be information or require an action. So, users can receive alerts & updates or take necessary action on-the-go, right from their mobile device, especially for approvals, eliminating the need to log into multiple web applications or it may just be used to access your QR code any time, for internal QR-code-based processes.
The application previously was meant only for Employees & was called “Employee Connect”, however, it was rebranded as “[24]7.ai Connect” on version 4.0 onwards. In current version, employees and non-employees can use the [24]7.ai Connect application, to do various tasks. Employees continue to do employee related tasks & view employee related screens, and non-employees can do only non-employee tasks & view only non-employee screens, like QR admin scanner for security/medical personals. Other than that, there are various application features such as WFH Attestation implemented on the request of the compliance team during Covid for WFH employees, QR Code solutions for WFO employees, News & Events, Dynamic Forms, Surveys, Covid Vaccine Registration/Trackers.
Collection and processing
For employees, the main purpose of the mobile application is to provide a single interface, especially managers & senior leadership, to be able to log into only one application and access notifications and take necessary action like approve/reject requests from anywhere, on the go, instead of logging into multiple sub-systems & their respective web-applications. For this, sub-systems use a framework of Web APIs provided/exposed to them, which they can send notifications to employees/users, which in turn are made available on the mobile application for employees to access & action as needed. They could be in the form of just read-only notifications, that need not be actioned. In addition to notifications, there are self-serve options that serve as an extension to the various sub-systems which employees can initiate requests, such as apply for leave, view leave balance, or raise an incident ticket and get geo WiFi password. Also, the ability to publish News & Events, and release surveys to employees, are features that help with employee engagement. During Covid, various Covid related enhancements like WFH Attestation, Vaccination Tracker, QR Code processes were implemented, that helped employees either for working from home, or working from office.
For non-employees, mainly QR Code scanning admins, the application helps them process employees via any QR Code based process, where employees show the QR code generated on their application & the admins use their application to scan the employees QR code and throw results or actions to be taken, like in the Medical Check process setup, for staying compliant in line with governmental authorities and to have checks in place to ensure Covid guidelines are followed. Also, for non-employees to have their own QR code to follow the QR code process.
What Personal Information we collect when Users download and login to our app?
For employees, post authentication with Network Terminal credentials, details pertaining to employees are retrieved and stored from Active Directory and Employee database for auto-logins. The details collected includes but not limited to:
- Employee ID
- Email ID
- Department
- User Type
- Geo
- Push registration ID
- User access token
- Contacts
- Files
- Location
- Camera
- Accounts
For non-employees, post authentication with local user ID (system generated) and password (set by user on first login). Details pertaining to non-employees are retrieved and stored from local Connect database, as configured by admins while creating their login ID. The details collected includes but not limited to:
- User ID
- Email ID
- User Type
- Geo
- Push registration ID
- User access token
- Contacts
- Files
- Location
- Camera
- Accounts
For all users, all these details are encrypted & stored in Keystore / Keychain. Device specific details such as UUID, OS version and device model are retrieved and securely stored.
How we protect your information?
We implement a variety of security measures when an employee enters, submits, or accesses their information to maintain the safety of your personal information. Your personal information is contained behind secured networks and is only accessible by a limited number of persons who have special access rights to such systems and are required to keep the information confidential. In addition, all employee related data are encrypted and stored in the apps Keystore (Android) or Keychain (iOS).
Cookies, IP Addresses and Other Tracking Technologies
We capture and store the IP address of user whenever they access the app. We also use an access token system that is unique for each user and expires post 24 hours. Google Firebase Analytics is integrated for tracking usage.
Disclosures to third parties
We use the Xamarin framework for developing the mobile app, which in turn provides various third-party plug-ins used in the application, including Google Firebase Analytics plugin. We do not sell, trade, or otherwise transfer your Personally Identifiable Information to outside parties, unless we provide users with advance notice. We ensure to take appropriate security measures to protect your personal data that require parties who process personal data on our behalf.
Opt out
You can uninstall the App to Opt-out of all the services that are provided via [24]7.ai Connect.
Accuracy of Personal Information
[24]7.ai intends to maintain accurate Personal Information at all times. If you require the Personal Information you have provided [24]7.ai to be updated, or that we delete inaccuracies you may send updates and corrections to [24]7.ai via email to IS-Support@247-inc.com specifying in the Subject line that you wish to provide an update and we will make reasonable efforts to incorporate the changes in our records as soon as practicable, if you provide the information we require to locate your Personal Information in our records (e.g. old name, email address, etc.). Once we make the requested update, we will send you an e-mail confirmation so that you are aware the update or correction has been made. If you requested to update your e-mail address, we will send the confirmation notice to both the old and new email addresses. If you wish to access your shared personal information, cancel your account or request that we no longer use your information to provide you services contact us via the information above. We will respond to your requests for access within a reasonable amount of time.
Statement of Consent
By using this App, you consent to the terms of this [24]7.ai Connect Privacy Policy and to [24]7.ai Inc., its affiliates and sub-processors, processing and using Personal Information for the purposes described herein.
Changes
We reserve the right to make changes to this Privacy Policy. It is advisable to review this privacy policy regularly so you are aware of these changes.
Contact Information
If there are any questions regarding this privacy policy, you may contact us using the information below.
Support Email ID: IS-Support@247-inc.com
South Africa (POPIA) Addendum
Last Revised on June 19, 2026
This addendum is intended to supplement the [24]7.ai’s existing Website Privacy Policy and applies to the processing of Personal Information relating to individuals in the Republic of South Africa, in accordance with the Protection of Personal Information Act 4 of 2013 (“POPIA”).
1. Application of this Addendum
This addendum applies where [24]7.ai collects and/or processes Personal Information from South African website visitors, customers, prospective customers, job applicants, contractors, employees, suppliers, or any other data subjects located in South Africa, or where [24]7.ai otherwise conducts processing activities subject to POPIA.
2. Responsible Party
For purposes of POPIA, [24]7.ai acts as the “Responsible Party” (or, where applicable, an “Operator”) in relation to the Personal Information processed through its website and related platforms.
3. Personal Information Collected
[24]7.ai may collect and process the following categories of Personal Information, depending on the nature of your interaction with the website:
- Identifiers and contact details (e.g., name, surname, email address, telephone number, physical address).
- Online identifiers and technical data (e.g., IP address, browser type, device identifiers, operating system, cookies, usage data, clickstream data).
- Recruitment and applicant information (e.g., CVs, employment history, education records, references, identity documentation where required).
- Customer support and communication data (e.g., correspondence, call recordings where applicable, enquiry submissions, chat transcripts).
- Business and transactional information (e.g., company name, job title, billing details, service preferences).
- Any other information you voluntarily provide through forms, portals, or communications with [24]7.ai.
4. Purpose of Processing (POPIA Section 18 Notice)
[24]7.ai processes Personal Information for the purposes set out in its Privacy Policy, including but not limited to:
- Providing products, services, and support.
- Responding to enquiries and communications.
- Facilitating recruitment and processing job applications.
- Improving website functionality, user experience, and security.
- Performing analytics and statistical reporting.
- Marketing and promotional communications (subject to applicable consent requirements).
- Complying with applicable legal and regulatory obligations.
- Preventing fraud, unlawful activity, and ensuring platform security.
Where Personal Information is collected directly from the data subject, [24]7.ai will take reasonable steps to ensure that the data subject is aware of the information being collected, the purpose for which it is collected, and any further information required by POPIA.
5. Voluntary or Mandatory Supply of Personal Information
The provision of Personal Information is generally voluntary. However, where Personal Information is required to provide products or services, respond to requests, administer contractual relationships, or process job applications, failure to provide the required information may result in [24]7.ai being unable to fulfil such request or relationship.
In certain circumstances, [24]7.ai may be legally required to collect specific Personal Information (for example, for employment, tax, or regulatory compliance purposes).
6. Lawful Grounds for Processing
[24]7.ai will process Personal Information in accordance with POPIA and only where a lawful justification exists, including:
- Where consent has been obtained.
- Where processing is necessary to carry out actions for the conclusion or performance of a contract.
- Where processing is required by law or permitted under applicable legal obligations.
- Where processing protects a legitimate interest of the data subject.
- Where processing is necessary for pursuing the legitimate interests of [24]7.ai or a third party, provided such interests are not overridden by the rights of the data subject.
7. Special Personal Information
[24]7.ai does not intentionally collect Special Personal Information via its website unless necessary for recruitment, employment, legal compliance, or where voluntarily provided by the data subject. Where Special Personal Information is processed, [24]7.ai will ensure that an applicable exemption or lawful basis under POPIA applies.
Special Personal Information may include information relating to health, biometric data, religious or philosophical beliefs, race or ethnic origin, trade union membership, criminal behaviour, or sex life, as defined in POPIA.
8. Sharing of Personal Information
[24]7.ai may share Personal Information with third parties as described in the Privacy Policy, including service providers, group companies, business partners, and regulators. Any sharing will be done in accordance with POPIA and subject to appropriate confidentiality, security, and contractual safeguards.
Where a third party processes Personal Information on behalf of [24]7.ai, such third party will be required to implement appropriate security measures and will be bound by an Operator Agreement or similar contractual terms where required.
9. Cross-Border Transfers (POPIA Section 72)
Where Personal Information is transferred outside of South Africa, [24]7.ai will ensure that such transfer is carried out in accordance with Section 72 of POPIA. This includes ensuring that the recipient is subject to laws, binding corporate rules, or agreements that provide an adequate level of protection substantially similar to POPIA, or that the data subject has consented to such transfer, or that the transfer is otherwise permitted under POPIA.
[24]7.ai will take reasonable steps to ensure that any cross-border recipient of Personal Information implements appropriate technical and organisational safeguards to protect Personal Information.
10. Direct Marketing
[24]7.ai may use Personal Information to contact you regarding products, services, recruitment opportunities, or updates. Where POPIA requires consent for direct marketing via electronic communications, [24]7.ai will obtain such consent prior to sending marketing communications.
You have the right to object to the processing of Personal Information for purposes of direct marketing at any time by using the unsubscribe functionality in marketing communications or by contacting [24]7.ai using the contact details below. [24]7.ai does not sell Personal Information to third parties.
Where [24]7.ai processes Personal Information relating to children or minors, such processing will be conducted in accordance with applicable privacy and data protection laws, including obtaining any required consent or authorization from a parent, guardian, or other legally competent person where required.
11. Security Safeguards (POPIA Section 19)
[24]7.ai will take appropriate, reasonable technical and organizational measures to secure the integrity and confidentiality of Personal Information in its possession or under its control, in accordance with POPIA. Such safeguards may include access controls, encryption where appropriate, monitoring of systems, secure storage, and secure destruction of Personal Information when no longer required.
[24]7.ai will take reasonable steps to ensure that Operators processing Personal Information on their behalf maintain similar security safeguards.
12. Retention and Destruction
[24]7.ai will retain Personal Information only for as long as necessary to fulfil the purposes for which it was collected, to comply with legal and regulatory obligations, for different audit requirements, or as otherwise permitted under POPIA. Once retention is no longer required, Personal Information will be securely destroyed, deleted, or de-identified, unless retention is required or permitted by law.
13. Data Subject Rights (South Africa)
In terms of POPIA, you have the right to:
- Request confirmation as to whether [24]7.ai holds Personal Information about you.
- Request access to Personal Information held about you.
- Request the correction, destruction, or deletion of Personal Information that is inaccurate, irrelevant, excessive, out of date, incomplete, misleading, or unlawfully obtained.
- Object to the processing of Personal Information on reasonable grounds, subject to lawful exceptions.
- Object to the processing of Personal Information for purposes of direct marketing.
- Withdraw consent where processing is based on consent.
- Lodge a complaint with the Information Regulator regarding an alleged interference with the protection of your Personal Information.
Requests relating to access to Personal Information and the exercise of data subject rights may be submitted in accordance with [24]7.ai’s PAIA Manual, which is available on the website. The PAIA Manual sets out the applicable procedures, requirements, and timelines for submitting requests and exercising your rights.
14. Complaints and Contact Details
If you have any questions, objections, or complaints regarding the processing of your Personal Information, you may contact the [24]7.ai’s Information Officer or Privacy Contact as follows:
15. Contact Us
Information Officer / Privacy Contact email Address : Informationofficer.SA@247.ai or Privacy@247.ai
You may also lodge a complaint with the Information Regulator (South Africa):
Email: POPIAComplaints@inforegulator.org.za
Postal Address: P.O. Box 31533, Braamfontein, Johannesburg, 2017
Physical Address: JD House, 27 Stiemens Street, Braamfontein, Johannesburg, 2001
South Africa (PAIA) Manual
Last Revised on September 10, 2026
Purpose of the PAIA Manual
This PAIA Manual is useful for the public to:- Check the categories of records held by a body which are available without a person having to submit a formal PAIA request
- Have sufficient understanding of how to make a request for access to a record of the body, by providing a description of the subjects on which the body holds records and the categories of records held on each subject
- Know the description of the records of the body which are available in accordance with any other legislation.
- Access all the relevant contact details of the IO and DIO who will assist the public with the records that they intend to access.
- Know the description of the guide on how to use PAIA, as updated by the Regulator, and how to obtain access to it.
- Know if the body will process personal information, the purpose of processing personal information, and the description of the categories of data subjects and of the information or categories of information relating thereto.
- Know the recipients or categories of recipients to whom the personal information may be supplied.
- Know if the body has planned to transfer or process personal information outside of the Republic of South Africa and the recipients or categories of recipients to whom the personal information may be supplied.
- Know whether the body has appropriate security measures to ensure the confidentiality, integrity and availability of the personal information which is to be processed.
Key Contact Details for Access to Information of the 247AI SOUTH AFRICA (PTY) LTD
Information Officer| Name | Johannes Christaan S |
| Email address | Informationofficer.SA@247.ai |
| Office address | 11 IMAM HARON ROAD CLAREMONT CLAREMONT WESTERN CAPE 7708 |
| Email address | Privacy@247.ai |
Guide on how to use PAIA and how to Obtain Access to the Guide
- The Regulator has, in terms of section 10(1) of PAIA, as amended, updated and made available the revised guide on how to use PAIA (“guide”), in an easily comprehensible form and manner, as may reasonably be required by a person who wishes to exercise any right contemplated in PAIA and POPIA
- The guide is available in each of the official languages and in braille.
- The aforesaid guide contains the description of:
- The objects of PAIA and POPIA;
- The postal and street address, phone and fax number and, if available, email address of:
- The IO of every public body, and
- Every DIO of every public and private body is designated in terms of section 17(1) of PAIA and section 56 of POPIA[1];
- The manner and form of a request for:
- Access to a record of a public body contemplated in section 11[2].
- Access to a record of a private body contemplated in section 50[3].
- An internal appeal.
- A complaint to the Regulator
- An application with a court against a decision by the IO of a public body, a decision on internal appeal or a decision by the Regulator or a decision of the head of a private body.
- The provisions of sections 14[4] and 51[5] requiring a public body and private body, respectively, to compile a manual, and how to obtain access to a manual;
- The provisions of sections 15[6] and 52[7] providing for the voluntary disclosure of categories of records by a public body and private body, respectively;
- The notices issued in terms of sections 22[8] and 54[9] regarding fees to be paid in relation to requests for access;
- The regulations made in terms of section 92[10];
- Assistance is available from the IO of a public body in terms of PAIA and POPIA;
- The assistance available from the Regulator in terms of PAIA and POPIA; and
- All remedies in law are available regarding an act or failure to act in respect of a right or duty conferred or imposed by PAIA and POPIA, including the manner of lodging.
- Members of the public can inspect or make copies of the guide from the offices of the public and private bodies, including the office of the Regulator, during normal working hours.
- The guide can also be obtained:
- Upon request to the IO.
- From the website of the Regulator (Empowered to monitor and enforce compliance by public and private bodies.)
- A copy of the guide is also available in the following three official languages, for public inspection during normal office hours:
- English.
- Afrikaans.
- Zulu.
Guide of Information Regulator
- A guide to PAIA and how to access information in terms of PAIA has been published pursuant to section 10 of PAIA.
- The guide contains information required by an individual who may wish to exercise their rights in terms of PAIA.
- Should you wish to access the guide, you may request a copy from the IO by contacting him/her using the details specified above.
- You may also inspect the guide at 247AI SOUTH AFRICA (PTY) LTD’s offices during ordinary working hours.
- You may also request a copy of the guide from the Information Regulator at the following details:
| Postal address | P O Box 31533, Braamfontein, Johannesburg, 2017 |
| Contact number | +27 (10) 023-5200 |
| Website | www.inforegulator.org.za |
| PAIAComplaints@inforegulator.org.za. |
Latest Notices in terms of Section 52(2) of PAIA
At this stage, no notice(s) has/have been published on the categories of records that are available without having to request access to them in terms of PAIA.Availability of Certain Records in terms of PAIA
Categories of records of the 247AI SOUTH AFRICA (PTY) LTD which are available without a person having to request access:| Category of Records | Types of the Record | Available on Website | Available on Request |
| PAIA Manual | Company’s current PAIA Manual | X | X |
| Company overview | Company profile, business activities (technology services, business support services, BPO/agent services), business activities, contact details) contact details | X | X |
| Policies (public-facing) | Privacy policy, website cookies policy | X | X |
| Legal disclosures | Disclaimers, terms & conditions, consumer protection notices related to logistics service agreements | X | X |
| News and announcements | Service updates, media releases, company news relevant to logistics/shipping/wagons/rail, changes in service offering | X | X |
| Public marketing materials | Brochures, descriptions of service offerings (road transport, rail, warehousing, cold chain, project cargo, etc.) | X | X |
| POPIA and PAIA awareness training certificates | Records of internal or external training / awareness sessions on data protection (POPIA) and access to information (PAIA) | – | X |
| Public tender or supplier information (if applicable) | Supplier onboarding requirements, procurement notices, B-BBEE certificate (if published), accreditation or certification documents | – | X |
| Contact information for IO | Name, designation, email address, telephone / fax / physical address | X | X |
| Category of Records | Applicable Legislation | Department/ Subject Area |
| Memorandum of Incorporation, company registration documents, minutes of board meetings, share register | Companies Act, 71 of 2008 | Corporate Governance |
| Employment contracts, employee attendance records, payroll information, leave records | Basic Conditions of Employment Act, 75 of 1997 | Human Resources (HR) |
| Disciplinary records, grievance procedures, union agreements, Commission for Conciliation, Mediation and Arbitration (CCMA) documentation | Labor Relations Act, 66 of 1995 | HR |
| Employment Equity (EE) plans, EE reports, committee meeting minutes | Employment Equity Act, 55 of 1998 | HR |
| Tax returns, IRP5 certificates, Pay-As-You-Earn (PAYE) records, employee tax submissions | Income Tax Act, 58 of 1962 | Finance |
| Workplace Skills Plans (WSPs), annual training reports, learnership agreements | Skills Development Act, 97 of 1998 | Training and Development |
| Unemployment Insurance Fund (UIF) contribution records, declarations, employee benefit claim records | Unemployment Insurance Act, 63 of 2001 | HR |
| Health and safety audits, incident reports, risk assessments, safety committee records | Occupational Health and Safety Act, 85 of 1993 | Occupational Health and Safety |
| Value-Added Tax (VAT) returns, input/output tax records, SARS correspondence | Value-Added Tax Act, 89 of 1991 | Finance |
| Workers Compensation Assistance (WCA) claims, injury-on-duty reports, compensation records | Compensation for Occupational Injuries and Diseases Act, 130 of 1993 | Occupational Health and Safety |
| B-BBEE certificates, ownership and supplier development records | Broad-Based Black Economic Empowerment Act, 53 of 2003 | Supply Chain Management (SCM) |
| Client contracts, complaint records, marketing disclaimers, product/ service terms and conditions | Consumer Protection Act, 68 of 2008 | Client Services/ Marketing |
| System access logs | Electronic Communication and Transactions Act, 25 of 2002 | IT Security |
| Incident reports | Electronic Communication and Transaction Act, 25 of 2002 | IT Security |
| Cybersecurity incident reports, phishing logs, malware reports, vulnerability assessments, system monitoring logs | Cybercrimes Act, 19 of 2020 | IT / Information Security |
| Call recordings, customer interaction records, scripts, voice recordings | Provision of Communication-Related Information Act, 70 of 2002 (RICA) | Operations / Compliance |
| Data subject consent forms, privacy notices, PAIA Manual, operator agreements, processing activity records | Protection of Personal Information Act, 4 of 2013 | Legal and Compliance |
| PAIA Manual, access request logs, training records | Promotion of Access to Information Act, 2 of 2000 | Legal and Compliance |
| Know Your Customer (KYC) documents, client identification and verification records | Financial Intelligence Centre Act, 38 of 2001 (if applicable) | Client Services/ Finance |
| Electronic communications policies, e-signature consents, website terms and conditions | Electronic Communications and Transactions Act, 25 of 2002 | Information Technology (IT) |
| Document retention and disposal schedules, archive logs | National Archives and Records Service Act, 43 of 1996 | Records Management |
- 247AI SOUTH AFRICA (PTY) LTD holds and/or processes the following records for the purposes of PAIA and POPIA:
- PAIA: PAIA Manual; PAIA guides; PAIA records; PAIA submission records; awareness training.
- POPIA: Including, but not limited to, the following: IO Registration Certificate; data breach records; retention records; awareness training.
- Further information may be made available upon request.
- The above-mentioned records may be requested; however, it should be noted that there is no guarantee that the request will be honored. Each request will be evaluated in terms of PAIA and any other applicable legislation.
Request Process
- An individual who wishes to place a request must comply with all the procedures laid down in PAIA.
- The requester must complete Form 02 of PAIA Forms (Request for Access to Record) herein, is attached hereto and submit it to the IO at the details specified herein.
- The prescribed form as well as payment of a request fee and a deposit (if applicable) must be submitted to the IO at/via the postal or physical address, fax number or email address as is stated herein.
- The prescribed form must be completed with enough particularity to enable the IO to determine:
- The record(s) requested;
- The identity of the requestor;
- What form of access is required; and
- The postal address or fax number of the requestor.
- The requestor must state that the records are required for the requestor to exercise or protect a right, and clearly state what the nature of the right is so to be exercised or protected. An explanation of why the records are requested is required to exercise or protect the right.
- The request for access will be dealt with within 30 (thirty) days from date of receipt, unless the requestor has set out special grounds that satisfies the IO that the request be dealt with sooner.
- The period of 30 (thirty) days may be extended by not more than 30 (thirty) additional days, if the request is for a large quantity of information, or if the request requires a search for information held at another office of 247AI SOUTH AFRICA (PTY) LTD and the information cannot be reasonably obtained within 30 (thirty) days. The IO will notify the requestor in writing should an extension be necessary.
- The IO must communicate a response to the request for access using Form 03 of PAIA Forms (Outcome of Request and of Fees Payable) herein. This communication shall inform the requestor of:
- The decision; and
- Fees payable.
- If the IO is of the opinion that the searching and preparation of the record for disclosure would amount to more than six (6) hours, he/she shall inform the requestor to pay a deposit not exceeding one third of the amount payable.
- Should the requestor have any difficulty with the form or the process laid out herein, the requestor should contact the IO for assistance.
- An oral request can be made to the IO should the requestor be unable to complete the form due to illiteracy or a disability. The IO will then complete the form on behalf of the requestor and provide a copy of the form to the requestor.
- Form 2 of POPIA Forms (Request for Correction or Deletion) herein, is used by a data subject to request the correction of inaccurate, outdated, incomplete, irrelevant, or misleading personal information, and/or the deletion or destruction of personal information that is no longer necessary or unlawfully obtained, in accordance with Section 24(1) of POPIA. It ensures that responsible parties maintain accurate and lawful records of personal data.
- Form 3 of POPIA Forms (Application for the Issue of a Code of Conduct) herein is used by an industry body, profession, or class of entities to apply for the issuance of a Code of Conduct under Section 61(1)(b) of POPIA. It allows industries to self-regulate how personal information is processed within their sector, in line with the conditions for lawful processing.
- Form 4 of POPIA Forms (Request for Consent – Direct Marketing) herein enables a responsible party to formally request a data subject’s consent to receive direct marketing communications via unsolicited electronic means (e.g., SMS, email), as required under Section 69(2) of POPIA. It ensures that individuals have control over whether and how they are marketed to.
- Form 5 of POPIA Forms (Complaint Regarding Interference with Personal Information) herein allows a data subject or complainant to submit a complaint to the IR concerning unlawful interference with personal information; or a determination made by an adjudicator under POPIA. It provides an avenue for recourse and investigation in cases of non-compliance with data protection obligations.
Grounds for Refusal
- The following are grounds upon which 247AI SOUTH AFRICA (PTY) LTD may, subject to the exceptions in chapter 4 of PAIA, refuse a request for access in accordance with chapter 4 of PAIA:
- Mandatory protection of the privacy of a third party who is a natural person, including a deceased person, where such disclosure of personal information would be unreasonable.
- Mandatory protection of the commercial information of a third party, if the records contain:
- Trade secrets of that third party;
- Financial, commercial, scientific or technical information of the third party, the disclosure of which could likely cause harm to the financial or commercial interests of that third party; and/or
- Information disclosed in confidence by a third party to 247AI SOUTH AFRICA (PTY) LTD, the disclosure of which could put that third party at a disadvantage in contractual or other negotiations or prejudice the third party in commercial competition.
- Mandatory protection of confidential information of third parties if it is protected in terms of any agreement.
- Mandatory protection of the safety of individuals and the protection of property.
- Mandatory protection of records that would be regarded as privileged in legal proceedings.
- Protection of the commercial information of 247AI SOUTH AFRICA (PTY) LTD, which may include:
- Trade secrets;
- Financial/commercial, scientific or technical information, the disclosure of which could likely cause harm to the financial or commercial interests of 247AI SOUTH AFRICA (PTY) LTD;
- Information which, if disclosed, could put 247AI SOUTH AFRICA (PTY) LTD at a disadvantage in contractual or other negotiations or prejudice 247AI SOUTH AFRICA (PTY) LTD in commercial competition; and/or
- Computer programs which are owned by 247AI SOUTH AFRICA (PTY) LTD, and which are protected by copyright and intellectual property laws.
- Research information of 247AI SOUTH AFRICA (PTY) LTD or a third party, if such disclosure would place the research or the researcher at a serious disadvantage
- Requests for records that are clearly frivolous or vexatious, or which involve an unreasonable diversion of resources.
Remedies Should a Request be Refused
If 247AI SOUTH AFRICA (PTY) LTD does not have an internal appeal procedure in light of a denial of a request, decisions made by the IO is final. The requestor may in accordance with sections 56(3) (c) and 78 of PAIA, apply to a court for relief within 180 (one-hundred-and-eighty) days of notification of the decision for appropriate relief.Fees
The following fees shall be payable upon request by a requestor:| Details | Fee |
| Request fee (payable on every request) | R140.00 once-off |
| Photocopy of an A4 page or part thereof | R2.00 per page |
| Printed copy of an A4 page or part thereof | R2.00 per page |
| Hard copy on flash drive (flash drive to be provided by requestor) | R40.00 once-off |
| Hard copy on a compact disc (compact disc to be provided by requestor) | R40.00 once-off |
| Hard copy on a compact disc (compact disc to be provided by 247AI SOUTH AFRICA (PTY) LTD) | R60.00 once-off |
| Transcription of visual images per A4 page | As per quotation of service provider |
| Copy of visual images | As per quotation of service provider |
| Transcription of an audio record | R24.00 per A4 page |
| Copy of an audio record on flash drive (flash drive to be provided by requestor) | R40.00 once-off |
| Copy of an audio on a compact disc (compact disc to be provided by requestor) | R40.00 once-off |
| Copy of an audio on a compact disc (compact disc to be provided by 247AI SOUTH AFRICA (PTY) LTD) | R60.00 once-off |
| Base/starting rate to search for and prepare the record for disclosure | R145.00 per hour for each hour or part thereof, excluding the first hour, reasonably required for such search and preparation (cannot exceed R435.00 per request) |
| Rate to search for and prepare the record for disclosure | R435.00 per hour for each hour or part thereof, excluding the first hour, reasonably required for such search and preparation (cannot exceed total cost) |
| Postage, email or any other electronic transfer | Actual expense, if any |
Processing of Personal Information
The purposes for processing personal information include:- To provide technology and business support services, including call handling, customer support services, sales support, and related client service functions.
- To respond to enquiries, complaints, claims, or service-related requests.
- To process payments for services rendered, including invoicing, billing, and reconciliations.
- To perform contractual obligations in terms of service agreements with clients, suppliers, and business partners, including compliance with service level agreements (SLAs).
- To conduct quality assurance monitoring, including call evaluations, performance reviews, service improvement reporting, and customer satisfaction feedback.
- For recruitment, onboarding, training, workforce management, and HR administration purposes, including verification of qualifications and work history.
- For security, access control, and identity verification purposes, including the accuracy of personal information provided.
- To maintain IT systems, network infrastructure, cybersecurity monitoring, and business continuity processes.
- To comply with applicable legal and regulatory requirements, including record retention obligations and lawful disclosure obligations.
- To conduct direct marketing activities where consent is obtained or where permitted by law, including the management of opt-outs and objection requests.
- To support dispute resolution, claims investigations, or regulatory reporting.
| Categories of Data Subjects | Personal Information that may be Processed |
| Customers/clients | Name, address, registration numbers or identity numbers, employment status and bank details, Physical Address |
| Service providers | Name, registration number, VAT number, address, trade secrets and bank details |
| Employees | Name, surname, ID number, tax number, contact details, residential address, bank details, employment contracts, payroll and benefits information, leave records, performance records, disciplinary records, qualifications, race and gender (for EE compliance), training and development records, health and safety information. |
| Job Applicants | Name, surname, contact details, CV, qualifications, previous employment history, references, criminal or credit checks (if applicable). |
| Contractors / Freelancers | Full name, identity number, contact info, banking details, tax information, contracts, work experience, qualifications |
| Visitors / Guests | Name, contact details, vehicle registration (if recorded), visitor registers, CCTV footage (if applicable for office/site security). |
| Regulatory Bodies / Authorities | Contact person details, company registration info, compliance documentation, correspondence records |
| Shareholders / Investors | Full name, contact info, identity numbers, banking info, shareholding details, investment history, correspondence records |
| IT / System Users | Full name, identity info, login credentials, access logs, device info, IP addresses, security authentication data |
| Marketing / Newsletter Subscribers | Full name, contact info (email, phone), preferences, consent records, interaction history with communications |
The Recipients or Categories of Recipients to whom the Personal Information may be Supplied
| Category of Personal Information | Recipients or Categories of Recipients to whom the Personal Information may be Supplied |
| Identity number and names, for criminal checks | South African Police Services (SAPS), accredited background check agencies |
| Qualifications, for qualification verifications | South African Qualifications Authority |
| Credit and payment history, for credit information | Credit bureaus, debt collection service providers |
| Employment history and references (for background checks) | Previous employers, recruitment agencies, background screening companies |
| Banking details | Financial institutions, payment processors |
| Health information (for occupational health assessments) | Occupational health service providers, medical professionals |
| Customs and import/export documentation (for cross-border logistics) | South African Revenue Service (SARS) Customs Division, international customs authorities |
| Security clearance information (for restricted access areas) | Security service providers, regulatory bodies |
| Skills development and training records | Sector Education and Training Authorities (SETAs) |
| CCTV footage and security incident records | Authorized security service providers; law enforcement authorities (if required) |
Planned Transborder Flows of Personal Information
247AI SOUTH AFRICA (PTY) LTD may transfer or store certain categories of personal information outside the Republic of South Africa, primarily using cloud-based service providers, payment gateways, marketing platforms, and IT hosting providers. These service providers may be located in jurisdictions such as the United States of America, the European Union, and other regions where global service providers host their systems.| The country in which personal information will be stored |
| India |
| Sout Africa |
- Keeping our systems secure through access controls, system monitoring, and usage tracking;
- Storing physical and digital records in secure, access-controlled environments;
- Restricting access to buildings, systems, and records to authorized personnel only;
- Securely destroying or deleting personal information once it is no longer required;
- Ensuring compliance with relevant data protection standards, legal requirements, and industry codes of conduct.
- Data encryption (at rest and in transit) to protect sensitive information from unauthorized access;
- Anti-virus and anti-malware software to detect, prevent, and mitigate cyber threats;
- Firewalls and intrusion detection/prevention systems (IDS/IPS) to monitor and safeguard network traffic;
- Multi-factor authentication (MFA) and role-based access controls to limit access based on job function and business need;
- Secure backup and disaster recovery solutions to ensure business continuity and data integrity;
- Ongoing system monitoring and access logging to detect and respond to suspicious activity;
- Physical security controls such as keycard access, secure storage, and visitor management procedures;
- Employee training and awareness program to promote secure data handling and prevent human error;
- Secure disposal of physical and electronic records when no longer needed or when required by law.
- These safeguards are continuously reviewed and enhanced to address new risks, changing business processes, and advancements in technology.
Availability of the Manual
- A copy of the manual is available:
- On or at any head office 247.ai 247AI SOUTH AFRICA (PTY) LTD for public inspection during normal business hours;
- To any person upon request and upon the payment of a reasonable prescribed fee; and
- To the Information Regulator upon request
- A fee for a copy of the manual, as contemplated in Annexure B of the Regulations, shall be payable per each A4-size photocopy made.
Objection to the Processing of Personal Information by a Data Subject
- A data subject who wishes to object to the processing of personal information in terms of section 11(3)(a) or section 11(3)(b) of the Act, must submit the objection to a responsible party at any time during office hours of a responsible party and free of charge.
- A data subject who wishes to object to the processing of personal information must do so on a form substantially similar to Form 3 herein, free of charge and reasonably accessible to a data subject by hand, fax, post, email, SMS, or WhatsApp and or in any manner expedient to a data subject in terms of section 11(3)(a) of the Act.
- A responsible party must, when collecting personal information of a data subject, notify the data subject, in terms of section 18(1)(h)(iv) of the Act, of their right to object, as referred to in section 11(3) of the Act.
- If an objection to the processing of personal information of a data subject is made telephonically, such an objection shall be electronically recorded by a responsible party and upon request, be made available to the data subject in any manner, including the transcription thereof.
Request for Correction/Deletion of Personal Information or Destruction/Deletion of Record of Personal Information
- A data subject has the right, in terms of section 24 of the Act, to request, where necessary, the correction, destruction, or deletion of his, her or its personal information.
- A data subject, who wishes to request a correction or deletion of his, her, or its personal information, as provided for in section 24(1)(a) of the Act, has the right to request correction or deletion of personal information at any time and free of charge, if the personal information is inaccurate, irrelevant, excessive, out of date, incomplete, misleading or obtained unlawfully.
- A data subject who wishes to request the destruction or deletion of a record of his, her, or its personal information in terms of section 24(1)(b) of the Act, has the right to request the destruction or deletion of a record of his, her or its personal information at any time and free of charge, if a responsible party is no longer authorised to retain such information in terms of section 14 of the Act.
- A request for correction to or deletion of personal information, as referred to in sub-regulation 12.11.2 or a request for the destruction or deletion of a record of personal information, as referred to in sub-regulation 12.11.3 must be submitted to a responsible party on a form which is substantially similar to Form 2 of POPIA Forms herein free of charge and reasonably accessible to a data subject by hand, fax, post, email, SMS, WhatsApp message or in any manner expedient to a data subject.
- A request for a correction or deletion of personal information by telephonic means shall be recorded by a responsible party and such recording must, upon request, be made available to a data subject in any manner, including the transcription thereof which shall be free of charge.
- A responsible party must, within 30 (thirty) days of receipt of the outcome of the request referred to in sub-regulation 12.11.2 or 12.11.3, notify a data subject, in writing, of the action taken as a result of the request
APPLICABLE FORMS
PAIA Forms
Form 01: Request for a Copy of the Guide from an Information Officer [Regulation 3]
Form 02: Request for Access to Record [Regulation 7]
Form 03: Outcome of Request and of Fees Payable [Regulation 8]
Form 05:Complaint Form [Regulation 10]
Form 13: PAIA Request for Compliance Assessment Form [Regulation 14(1)]
POPIA Forms
Form 1: Objection to the Processing of Personal Information
Form 2: Request for Correction of Deletion of Personal Information or Deletion of Record of Personal Information
Form 3: Application for the Issue of a Code of Conduct
Form 4: Application for the Consent of a Data Subject for the Processing of Personal Information for the Purpose of Direct Marketing
Form 5: Complaint Regarding Interference with the Protection of Personal Information for the Purpose of Direct Marketing
Frequently Asked Questions
When providing services to a customer, [24]7.ai may transfer personal data outside of EEA, Switzerland and UK in its capacity as processor. The General Data Protection Regulation (GDPR) has been incorporated into UK’s domestic legislation, and therefore the data transfer mechanism permitted under the GDPR for transfers of personal data.